
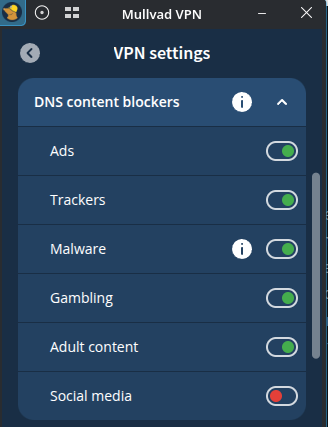
If you’re not running your own recursive DNS servers, this looks like a solid option. Myself, on the home network I run Pi-Hole/Unbound recursive DNS servers distributed to clients by my router, and when using Mullvad VPN I’m using their DNS servers that offer the same services with blocklists for ads, telemetry, malware… The really interesting bit was that Quad9 is being sued in the EU to have them block domains connected to copyright infringement, though I’m sure governments would like to expand that eventually. Quad9 has won one lawsuit, but have a new one to deal with. And you’d have to wonder if this is to financially penalize their non-profit to prevent further privacy measures. By default the Quad9 primary DNS server includes malware blocking, 9.9.9.9, or you can use unfiltered internet with 9.9.9.10. I’d use the ECS DNSSEC 9.9.9.11, backup 149.112.112.11 that include malware blocking. I was going to make a donation to Quad9, but you have to identify yourself even if using Bitcoin. Probably regulatory, but I just don’t do that and it’s not necessary and defeating the purpose of using Bitcoin.
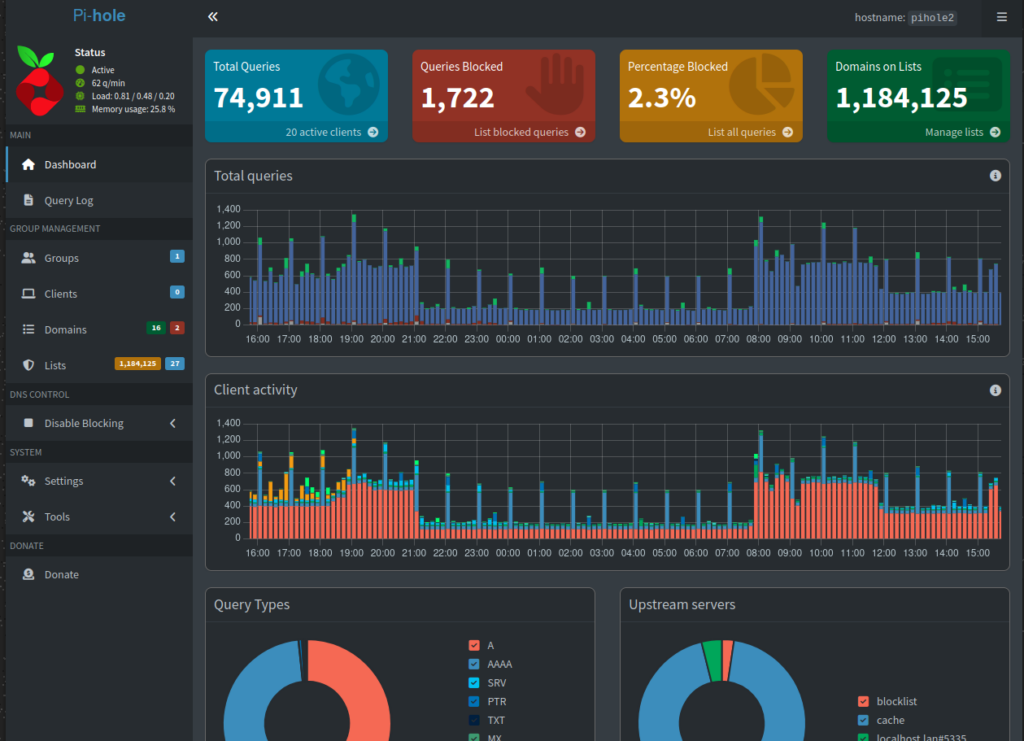
And to show how important your DNS server is, this is my primary Pi-Hole server with traffic for the last 24 hours on my home network. Though I have a bunch of computers and devices on my network. And if you’re running your own Pi-Hole/Unbound DNS, https://firebog.net/ has a list of blocklists you can add to your installation.